Logging is easy to enable and hard to use well. Many teams collect far more data than they can realistically review, then discover during an incident that the one field they needed was not captured. Useful logging is less about volume and more about intention. The question is not “Are we logging everything?” but “Can we answer the questions that matter when the time comes?”
Start by identifying the events that deserve attention: authentication successes and failures, privilege changes, administrative actions, configuration updates, and access to sensitive systems. Those records create the backbone of investigation and troubleshooting. From there, make sure timestamps are reliable, sources are consistent, and retention aligns with your operational and compliance needs. A log that disappears too quickly is only marginally better than one never captured.
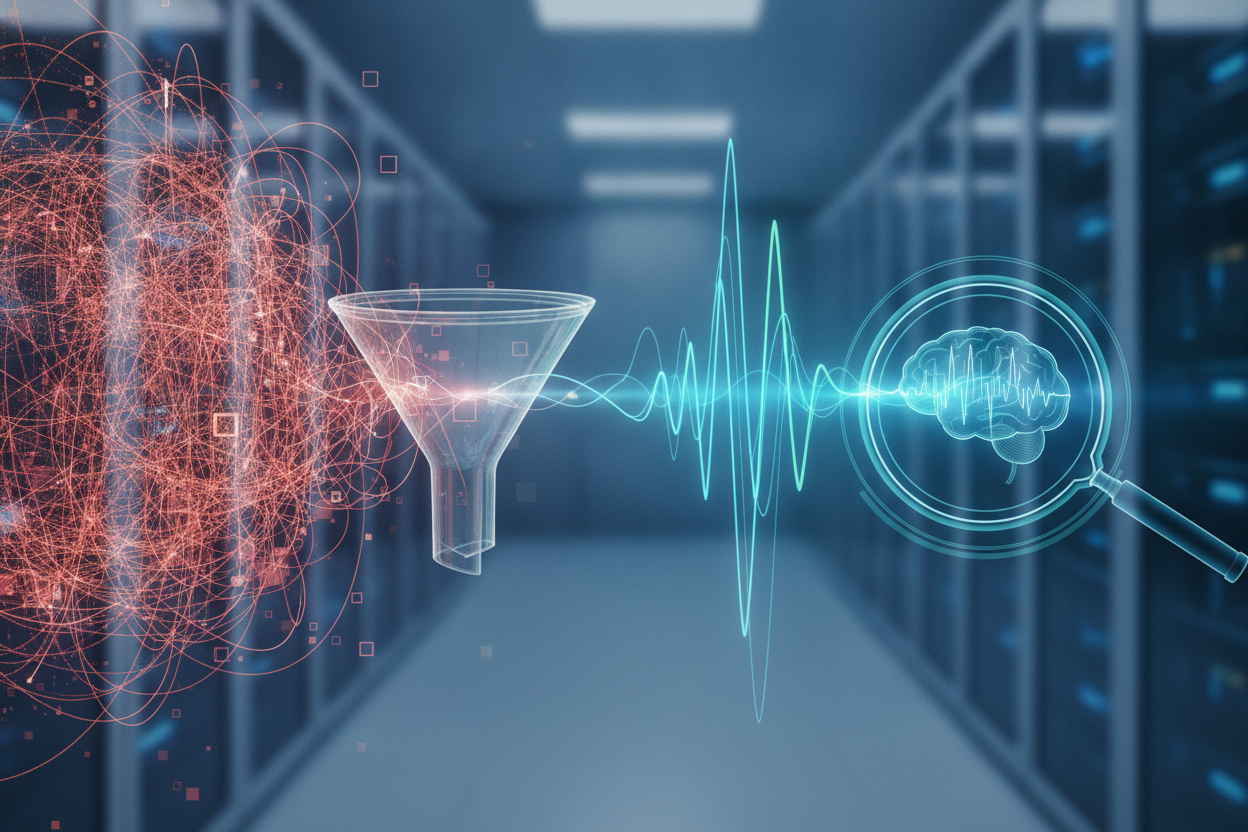
It also helps to think about noise reduction. If every normal event looks urgent, people stop paying attention. Tuning alerts, normalizing formats, and documenting expected behavior can make log review much more effective. The goal is not to eliminate all chatter, because systems are noisy by nature. The goal is to preserve signal and make unusual activity stand out.
Good logging supports both security and calm. It shortens root cause analysis, improves accountability, and gives teams something concrete to work with when memory is unreliable. In practice, that is often the difference between a quick answer and a long afternoon of polite guessing.
Leave a Reply